If you’re going to sell “lobster salad” in your store, it is a very good idea to make sure that your “lobster salad” contains actual lobster.
No, I’m not convinced by the argument that crawfish is close enough to lobster for it to count.
If you’re going to sell “lobster salad” in your store, it is a very good idea to make sure that your “lobster salad” contains actual lobster.
No, I’m not convinced by the argument that crawfish is close enough to lobster for it to count.
Added links to the following presentations:
“Earth vs. The Giant Spider”: This was described as a collection of weird, bizarre, freaky, and unusual hacks compiled by the presenters during penetration tests. I figured this would probably be a high energy, lots of fun, lots of laughs panel. I ended up kind of disappointed. Maybe high energy is too much to expect at 10 AM on DEFCON Sunday, but the presenters seemed curiously subdued. (This may have had something to do with non-functional equipment that resulted in them having to drop the live penetration test portion of the presentation.)
As for the hacks…well, okay, owning an entire country’s credit card processing (bypassing the firewall by sending packets from source port 0) is kind of cool. Getting cheap food from a restaurant chain by hacking a Javascript that communicates with a 3rd party server, and doesn’t validate data being sent from the restaurant’s website to the server? Meh. The story about cloning the support mailbox on an old ROLM PBX (default field service user ID/password) which ended up with the penetration testers doing Checkpoint support for one of the corporate users? Mildly funny. The other hacks (doing a HTTPS man in the middle attack with a self-signed certificate, and using information gathered that way to hijack a session to an external VPN by cloning cookies; high-def IP cameras with undocumented default accounts located right over keyboards, Oracle session hijacking), well, maybe you just have to have been there.
As for the “Caucasian-American love hack” (in which they were able to guess an admin’s password from his profile on an Asian-American dating site), I felt more pity for the poor admin, who was probably just looking for love (and not even in all the wrong places) rather than admiration for the penetration testers. Sorry, guys: I know your intentions were good, but this didn’t click with me. It may just have been a personal thing: YMMV.
“Seven Ways to Hang Yourself with Google Android”: An excellent presentation by Yekaterina Tsipenyuk O’Neil (Fortify) and Erika Chin (UC-Berkeley) about the major mistakes programmers making developing Android applications. Specifically:
(Edited to add 8/10/2011: I’ve added a link to the final version of this presentation.)
“Build your own Synthetic Aperture Radar”: So this wasn’t as dangerous as I expected (the radar is low-power) and it wasn’t quite as awesome as I expected. But this was a decent presentation on radar technology, starting with an overview of basics and proceeding onwards to discussion of a homebrew radar system.
One minor problem with this presentation was that the presenter (Michael Scarito) had converted his system to use a custom-built data acquisition board (previous versions used a sound card and MATLAB) and didn’t have build documentation for that board prepared yet. However, much of Mr. Scarito’s work is based on other work done at MIT. The slides for the talk are not currently online, as far as I know, but here’s a link to a MIT Open Courseware presentation that gives exact, step-by-step detail, parts lists, and other resources for a very similar project (cited by Mr. Scarito in his presentation).
“Wireless Aerial Surveillance Platform”: UAVs are fun. UAVs that have onboard computing power to crack WEP encryption are more fun. UAVs that add the ability to spoof cellular base stations are even more fun. UAVs that have the ability to communicate with a remote server and offload heavier computational tasks (like attacking WPA) are perhaps the most fun of all. Note: the link above doesn’t go to slides, but to the build blog maintained by the two presenters (Mike Tassey and Rich Perkins). The build blog provides a lot more detail than the presentation, and includes resource links. Very well done, gentlemen.
“SCADA & PLCs in Correctional Facilities: The Nightmare Before Christmas”: Borepatch posted a few days ago about a presentation at Black Hat on SCADA vulnerabilities. You could consider this the other shoe dropping.
Summary: many prisons and jails depend on programmable logic controllers (PLCs) to do things like unlock and unlock cell doors. Usually, these PLCs are all controlled from a central control center, so all you have to do, once you find a PLC vulnerability to exploit, is to get your exploit code into the central control center.
“But they aren’t connected to the Internet, right?” Sometimes they are: the systems need to get updates, or send information to other systems, or communicate with other people (food service vendors, for example). Sometimes the systems aren’t connected to the Internet, but other systems they connect to are. (The presenters cited one example where someone was able to upload arbitrary files to the wireless system on a patrol car, and from their to a central jail control system.) Someone could carry an exploit in on a USB drive.
“But the people who run these systems don’t go out to arbitrary sites, right?” The presenters cited examples, from their personal experience, of correctional institution employees watching videos on the Internet, checking GMail accounts, etc. Friend the right correctional institution employee on Facebook…
“But they couldn’t do anything bad, right? I mean, if they open the cell door, the control panel shows it, and won’t the guards catch them?” As for the guards catching them, I remember a story from Pete Earley’s book The Hot House: Life Inside Leavenworth Prison
(“Christ, what an imagination I’ve got.” Spot the reference, win a cheese.)
(Edited to add 8/10/2011: I’ve added a link to a white paper by the presenters that pretty well summarizes their presentation and findings.)
That concludes my DEFCON 19 roundup. As more of the presentations get online, I’ll be adding links to them, and there will probably be one or two update posts. If you attended a panel I missed at DEFCON 19, and think it is worth linking to, please feel free to mention it in the comments. Responses from presenters are also welcome, especially if I mis-represented or misunderstood a point.
Closing ceremonies ran a little long last night, and I went to bed pretty much immediately after they ended. I seem to be coming down with a cold or allergies or some sort of creeping DEFCON crud.
Please bear with me; I’m about to check out and leave for the airport, but I’ll have the notes for the last day up as soon as I possibly can.
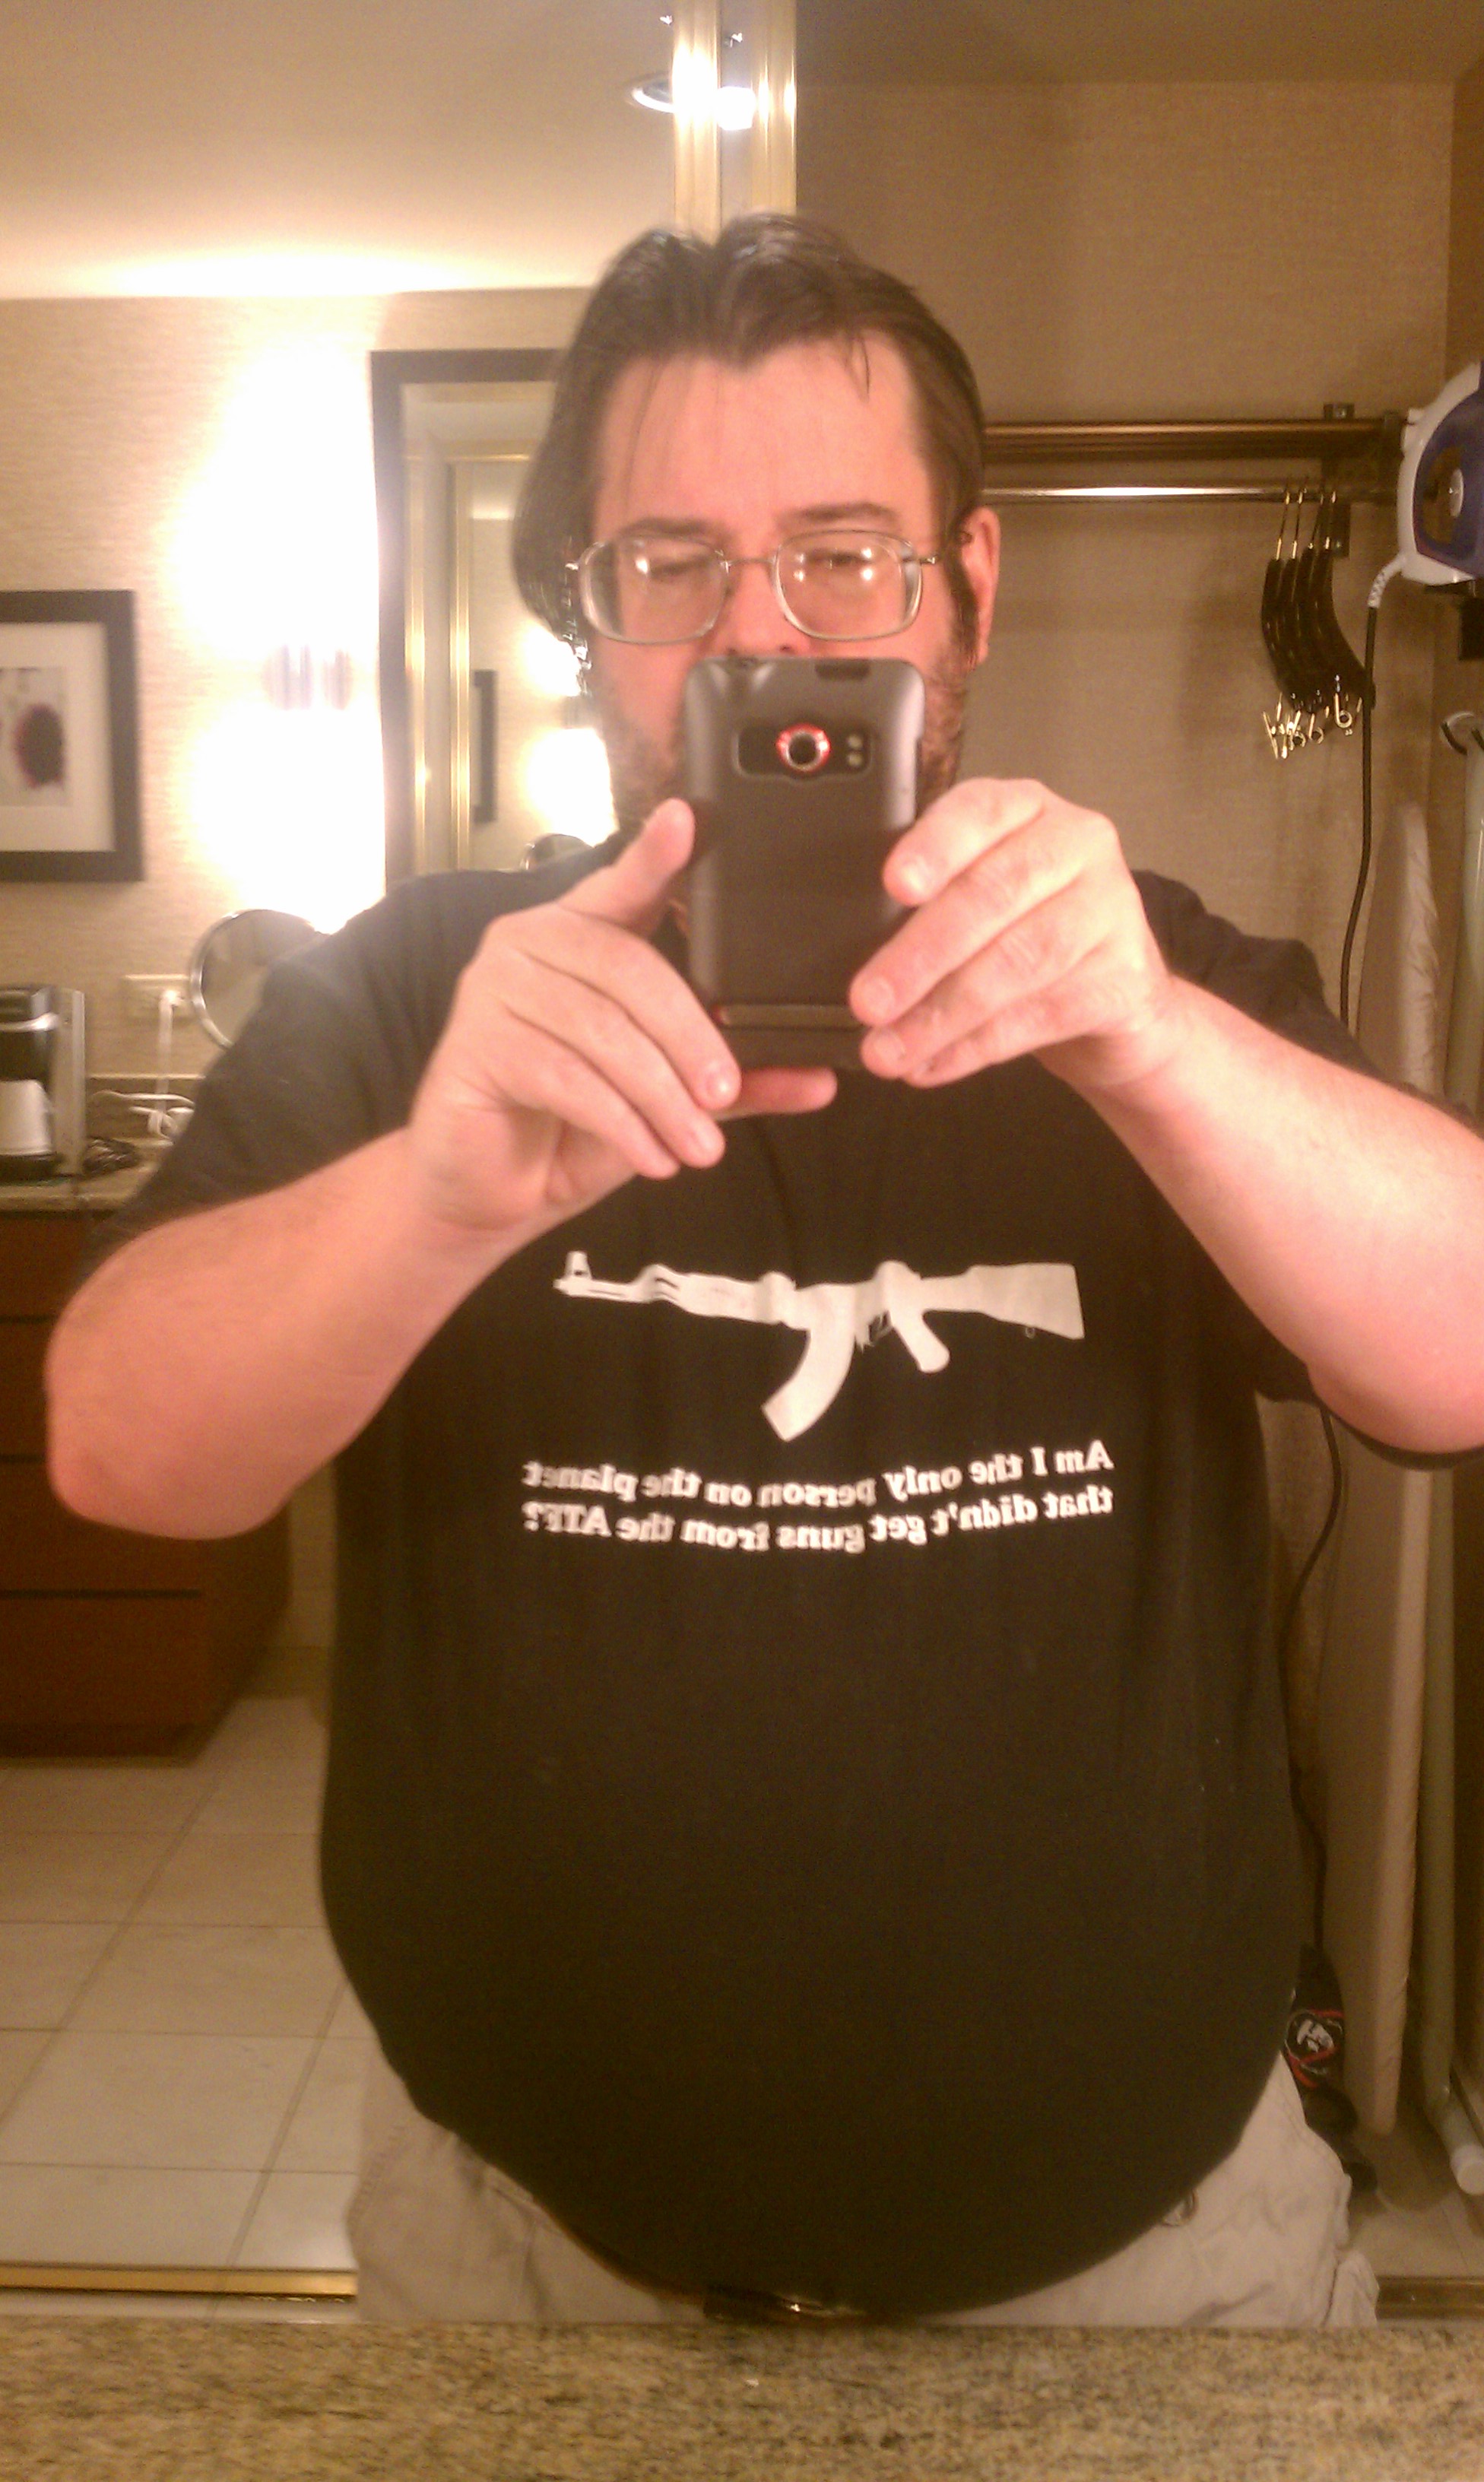
What the well-dressed gun blogger is wearing at DEFCON 19:
“Safe to Armed in Seconds: A Study of Epic Fails of Popular Gun Safes“: Confession time. I didn’t just watch this panel, I actually volunteered for part of it. I don’t think that compromised my objectivity, but better to be up front about it.
Deviant Ollam’s presentation concentrated on the smaller handgun safes, specifically the GunVault Microvault MV500, the BioBox, and the LokSAF PBS-001. Summarizing:
“DIY Non-Destructive Entry“: I missed this and “Battery Firmware Hacking” because I was still caught up in stuff from the gun safes panel. Sorry.
“Smile for the Grenade! ‘Camera Go Bang!’“: Nice guys, good presenters, total failure. The basic idea was to build a clone of military throwable/launchable video camera systems, using off-the-shelf parts (including the perfectly legal and not a destructive device at all 37mm grenade launcher) at a fraction of the cost. This looks like it could be a promising project, but the presenters only started working on it three months before the con, and only did their first test run the weekend before DEFCON. It didn’t go well; the powder they used to load their grenades was apparently defective, and they got no video. While it is interesting to see how small (and cheap!) wireless video cameras have gotten ($20 for the cameras they used, and $80 for the receiver), this is a presentation that should have been shelved for a future DEFCON.
“This is REALLY not the droid you’re looking for…”: From those wonderful folks who brought you Android rootkits, yet another Android exploit. Summary: because of Android’s design, and Google’s lack of strict enforcement of their user interface guidelines, it is possible to build an app that:
This is a very high level summary; the authors went into much more detail about how to build this kind of application in their talk. And it’s not really easy to fix the problems that enable an application of this sort without changing both the Android OS and the way Google/the Android Market does things.
“Welcome and the Making of the DEF CON 19 Badge”: didn’t bother going. I don’t care much about the making of this year’s badge.
“WTF Happened to the Constitution?”: perfectly fine talk. Except for some of the case law theprez98 referenced, pretty much everything he covered was already familiar to me from “The Agitator” and “Hit and Run”. That’s not his fault, though, and I’m sure a lot of what he covered was new to the rest of the audience. I was also previously unaware of The Assault on Privacy, and will have to add that to my blogroll.
“From Printer To Pwnd”: This was a fun little talk, covering multi-function printers and the vulnerabilities they introduce into networks. Basically, people get sloppy with these devices and fail to do things like change default passwords; also, many of these devices have bugs in the embedded firmware. The presenter, Deral Heiland, demonstrated some interesting attack vectors: “malformed” URLs which allow you to bypass authentication on certain devices, “information leakage” attacks which allow you to get useful information (like passwords) out of the web admin pages, “forced browsing” attacks which allow you to grab device address books (which may also contain passwords), and “passback attacks” which trick the device into communicating with an attacker (for example, using LDAP configuration script testing). All of this culminated in the release of Praeda, an automated toolkit for attacking multi-function devices. The latest version can be found here: I don’t have a link to the slides, but will add one when I do.
“Black Ops of TCP/IP 2011“: You know how people talk about wanting the old funny Woody Allen back? This was the old funny Dan Kaminsky back; the guy who does deep arcane magic with TCP/IP packets and DNS.
His talk broke down roughly into three parts:
“And That’s How I Lost My Eye“: the funniest panel I went to today. Deviant Ollam, Bruce Potter, and Shane Lawson wanted to see if it was possible to destroy a hard drive in less than 60 seconds such that the data was unrecoverable, without setting off alarms or damaging any nearby humans, and without spending a lot of money on something like the SEMShred.
Ollam took the explosives/incendiary part of the equation. His results can be summarized as: it might be possible to use explosives, especially the popular “boomerite” type explosives used in exploding targets, to destroy a hard drive. But playing around with explosives, especially when you’re activating them electronically, is a good way to attract the attention of unpleasant people with badges. Apparently, those same people have no problems with explosives triggered by a rifle bullet, so if you want to affix an M1A above your server with a ton of “boomerite” below, go ahead…
Chemical methods didn’t work out very well either. Cobalt isn’t highly reactive, and the type of acids that can quickly dissolve a hard drive platter aren’t easily available at Home Depot and don’t play well with people and other living things. There were a lot of slides of vats of acid doing nothing to hard drive platters.
It’s also hard to destroy a drive physically. Hole saws, spade bits, and grinders did nothing.
The presenters did discover that a combination of a salt solution and electricity could strip the plating off of ceramic platter drives. But that didn’t work on aluminum platter drives.
What finally did work was fire. Propane and MAPP gas (which you can’t get in the US any more) will melt aluminum, but it’s hard to apply those to a spinning drive and have it melt; the spinning drive tends to dissipate heat. The presenters were working on an automated solution involving a glow plug, propane, and an Arduno, but ran out of time before they could finish that project.
However, you don’t have to melt a drive to render it unreadable; you only have to heat it to the Curie point. That’s not quite as spectacular as a spinning drive throwing off chunks of molten aluminum, but it will work. (However, if I understand Wikipedia right, the Curie point of colbalt is 1100 degrees C, and the melting point of aluminum is 660 degrees C. So I’m not sure what that buys you.) I wonder:
“Key Impressioning“: I can’t give this panel a fair evaluation. In brief, impressioning consists of sticking a blank key into a lock, moving the blank up and down, removing it, noting where the lock pins hit the key, filing down the contact points, and repeating the process until all the pins reach the proper depth and you have a working key. The presenter gave a live demo of this process, and was impressively quick at it.
The problems I had with this panel were:
So far, things have been relatively smooth. Just a few minor problems; I left a couple of things behind in Austin, but nothing that I can’t make do without.
There have been a couple of slightly unpleasant surprises. I discovered yesterday that one of my other favorite restaurants in Las Vegas, the Tillerman, abruptly closed in February. Google turned up this account of events from the Las Vegas Weekly: there’s a lot I disagree with in it (the neighborhood doesn’t strike me as being particularly sketchy, for example) but it is the best account I’ve been able to find.
I do have a badge, and I only had to wait in line two hours to get it. The other slightly unpleasant surprise, though, was that DEFCON decided that electronic badges are “passé”: this year’s badges are inert hunks of titanium, tied in with some sort of “puzzle based reality game”. (Joe Grand’s big enough to take care of himself, but the reference to “gameboy on a string” in the DEFCON program seems to me to be a nasty, though perhaps unintended, slap.)
Last night, I decided to try a place I’ve been driving past and thinking of trying since…oh, about 2000 or so. Yes, I know they’re a chain, but have you ever been to a Lawry’s The Prime Rib? Did you even know Lawry’s had restaurants, or were you just familiar with their seasoning salt? (There’s four Prime Ribs in the US: Vegas, Chicago, Beverly Hills, and Dallas.)
Having finally crossed that off my list, I have to say I’m glad I went. The Prime Rib’s an interesting place; the decor (at least in Vegas) reminds me of photos I’ve seen of Chasen’s and other old star hangouts in Los Angeles. And the whole experience has a certain…theatricality to it that’s missing from pretty every restaurant in existence today. Your waiter preps your salad in a spinning salad bowl at the table. When you’re ready for your meal, a carver comes by with a massive polished steel cart and cuts your prime rib off of what must be at least half a cow right in front of you. Plus there’s mashed potatoes and honest-to-Ghu Yorkshire pudding served with it. I think my late stepfather would have loved this place. He was a big prime rib fan, but I think he also would have gotten a kick out of the whole sort of…vintage experience, is the best way I can think of to describe it.
I’ve never really thought of Las Vegas as a bookish town, but Lawrence tipped me off to two vintage bookstores that I visited today. I heartily endorse both of them, and strongly recommend that you visit both. Doing so is pretty easy, as they’re basically right across the street from each other.
I’m sorry I didn’t catch the name of the gentleman who runs Greyhound’s Books, but he came across to me as someone who’s very much worth knowing. I wouldn’t describe him as “kind”, as I so often describe others; he seems intolerant of the rude, the willfully ignorant who wish to remain so, and others who would waste his time. (While I was there, he literally chased one person out of the store for using a cell phone.) But for the serious and polite book shopper, this store is a delight. He seems to be very strong on mystery, military history, and history in general. His food and cooking selection also seemed strong to me; he had the only copy of Cross Creek Cookery I’ve seen in probably five years of searching. (The owner also writes, along with other folks, at Books of Worth, an entertaining site I was previously unaware of.)
I didn’t want to press for details (I’m not sure it is any of my damn business) but Amber Unicorn Books appears to be related in some way to Greyhound’s Books. I didn’t have as much interaction with the owners there as I did with the Greyhound’s Books owner, but they certainly seemed like very nice folks. Amber Unicorn appears to be stronger in paperbacks, especially genre paperbacks, but also has a good stock of history, mystery, and law/true crime.
One thing that really struck me about both stores; the folks at both knocked 10% off the total of my purchases for no apparent reason, other than (I guess) I was reasonably polite and didn’t use my cellphone or urinate on their rugs. They didn’t have to do that, and it was very much appreciated.
(And it helped, especially at Amber Unicorn. They had a copy of Skeeter Skelton’s Good Friends, Good Guns, Good Whisky, a book I didn’t even know existed until today. I’ve written before about the gun writers I read growing up; I remember Skelton’s stories with great fondness. Especially the one reprinted in this volume about Dobe Grant and his crate full of Colt Single Action Army parts. When I read that for the first time, man, I wanted a vintage Single Action Army. Still do, come to think of it. I don’t want to say what I paid for that book; let’s just say “Nostalgia is a moron” and leave it at that.)
If you’re a serious book person, you have to visit both of these stores if you’re ever in Las Vegas.
Me get up early and travel most of day.
Me spend much of rest of day driving around getting me Vegas legs back.
Me tired.
Me talk like Thag from “Far Side” due to travel and being tired.
Me sincerely hope Gary Larson having a wonderful life wherever he may be.
You come back tomorrow. Maybe some blog for you than.
The Texas Department of Transportation is closing the ramp from northbound 183 to southbound Loop 1 this coming weekend. The closure is supposed to start at 9 PM Friday, and run until 5 AM Monday.
TXDOT does have a pretty good reason for the closure; they’re repairing a section of the highway damaged in a horrible tanker truck accident/explosion last fall.
Lawrence pointed out that I hadn’t trolled the crowd for panel suggestions yet, and the schedule is up. Here’s the stuff I’m tentatively planning to see.
I’m open to requests, but I won’t make promises.
I’ll bring the cheese. His Gruberness has already brought the whine.
There’s two funny things about this. The first one: if you read the entire article, the Shifty Jelly people were fully aware going in that they weren’t going to make any money off of being the “free app of the day”, and had a chance to reject the offer…
And now you’re complaining?
Here’s the other funny thing. I’m one of those 101,491 people who downloaded Pocket Casts when it was free. I’m glad I did; if I had paid $2.70 for that app, I would have been very unhappy. Pocket Casts “works”, in the sense that it manages my podcast subscriptions and lets me play back podcasts.
But it’s buggy. For example, when I first start Pocket Casts, it frequently tells me there’s no podcasts playing. Sometimes that’s true; other times, I quit out of Pocket Casts during a podcast, so I’d expect it to show me the last podcast I was playing. Even better, when I select a podcast from the ones I’ve downloaded, Pocket Casts just displays the same “no podcasts playing” message. Repeatedly. No matter how many times I select a podcast; any podcast, I get the same “no podcasts playing” message. The only way I’ve found around this problem is to actually quit and relaunch the Pocket Casts application.
Good luck, guys. Don’t let the door hit you where God split you.
I really wish I could find that original Bloom County strip, but I digress.
The plan to build a new stadium for the New York Islanders failed. Overwhelmingly.
(Newsday has a pay wall set up, but the first two paragraphs are really the relevant part. ETA: here’s the NYT coverage.)
Yes, Michele Catalano has another “I”, “I”, “I” post up already.
…
We’re all Islanders. Don’t we all want what’s best for our communities? Perhaps not.
Because reasonable disagreement about whether subsidizing a professional sports team is a good idea equates to not “wanting what’s best for our community”.
Edited to add: I didn’t pick up on this right away.
So all along, you’ve been agitating for other people to pay the bills for your hockey team, Catalano, knowing full well that you’d be moving away and not having to deal with the tax burden you wanted to impose on other people in Nassau County? This explains much.
…to the previous post:
American McCarver: absolutely no mention of Hideki Irabu. Mike Monterio did find time to reblog an old article about Andre the Giant from Modern Drunkard.
Grantland, the heavily hyped Bill Simmons led ESPN spinoff: absolutely no mention of Hideki Irabu. Wright Thompson did find time to write about the death of William Faulkner’s niece, and Jay Caspian Kang found time to write about Amy Winehouse. (Edited to add: to be fair, Kang’s piece was published before Irabu’s death.)
Right Field, the National Review Online spin-off sports blog: absolutely no mention of Hideki Irabu.
You would think someone would acknowledge, even if just in passing, the suicide of a starting pitcher for the New York Yankees at the relatively young age of 42.
Yeah, Michele Catalano is at it again, trying to convince people they should vote for a new stadium for the New York Islanders. (Previously on WCD.) It is a curious article, full of “I want” and “I won’t” and “I”, “I”, “I”. It is as if Catalano thinks Long Island and Nassau County revolve around Catalano and her wants; as if everyone should just give in and let her have her beloved Islanders, because…
The idea that other people have wants, too, and those wants include things like wanting to keep the money they’ve earned (instead of putting it into the pockets of team owners so people like Catalano can “…get in my car fifteen minutes before game time and be in my seat with a pretzel and Coke before the puck drops”) seems never to have crossed Catalano’s mind.
Meanwhile, the indispensable Field of Schemes links to an interesting Montreal Gazette article about the deal. The Islanders are projecting $229 million a year in revenue if the referendum passes and a new stadium is built.
…is brought to you by Central Falls, RI.
Receiver Robert G. Flanders announced the step at City Hall Monday.
(Simpsons mode ON)
Stupid Flanders.
(Simpsons mode OFF)
I used to spend a fair amount of time in Rhode Island. (There’s a reason this blog has a “Rhode Island” tag. Actually, two reasons, but Buddy Cianci’s been quiet recently.) I don’t recall ever going through Central Falls; looking on Google Maps, it appears to be to the north of my old stomping grounds, closer to Pawtucket than Providence.